CMMC 2.0
Structured CMMC Readiness
CMMC 2.0 is the cybersecurity framework used to support eligibility for many US defence contracts. For organisations operating in the defence supply chain, failure to demonstrate appropriate readiness can create commercial and contractual risk. Spartacus Insights helps create a clearer, more defensible view of CMMC readiness by connecting assessment, evidence, reporting, and improvement activity in one governed model.

Defensible Delivery
CMMC 2.0 is strongest when it is used to build structured, evidence-backed readiness over time rather than treated as a reactive exercise shortly before contract activity demands it. It helps organisations strengthen cybersecurity practice in a way that supports defensible readiness rather than one-off compliance preparation.
That value is often lost when CMMC becomes a narrow assessment event focused only on getting through reviews. Spartacus Insights helps keep CMMC connected to broader delivery and improvement activity, so readiness can be built, evidenced, and sustained more consistently over time.
Consistent Judgement
As CMMC 2.0 is delivered across teams, clients, and repeat assessment cycles, interpretation can vary and evidence quality can drift. That makes Pass / Fail outcomes harder to compare, harder to defend, and more dependent on individual ways of working than they should be.
Spartacus Insights provides a more structured and governed way to deliver CMMC, helping teams assess practices more consistently, keep evidence in context, and produce Pass / Fail outcomes that remain easier to explain, review, and defend across repeat assessment cycles.
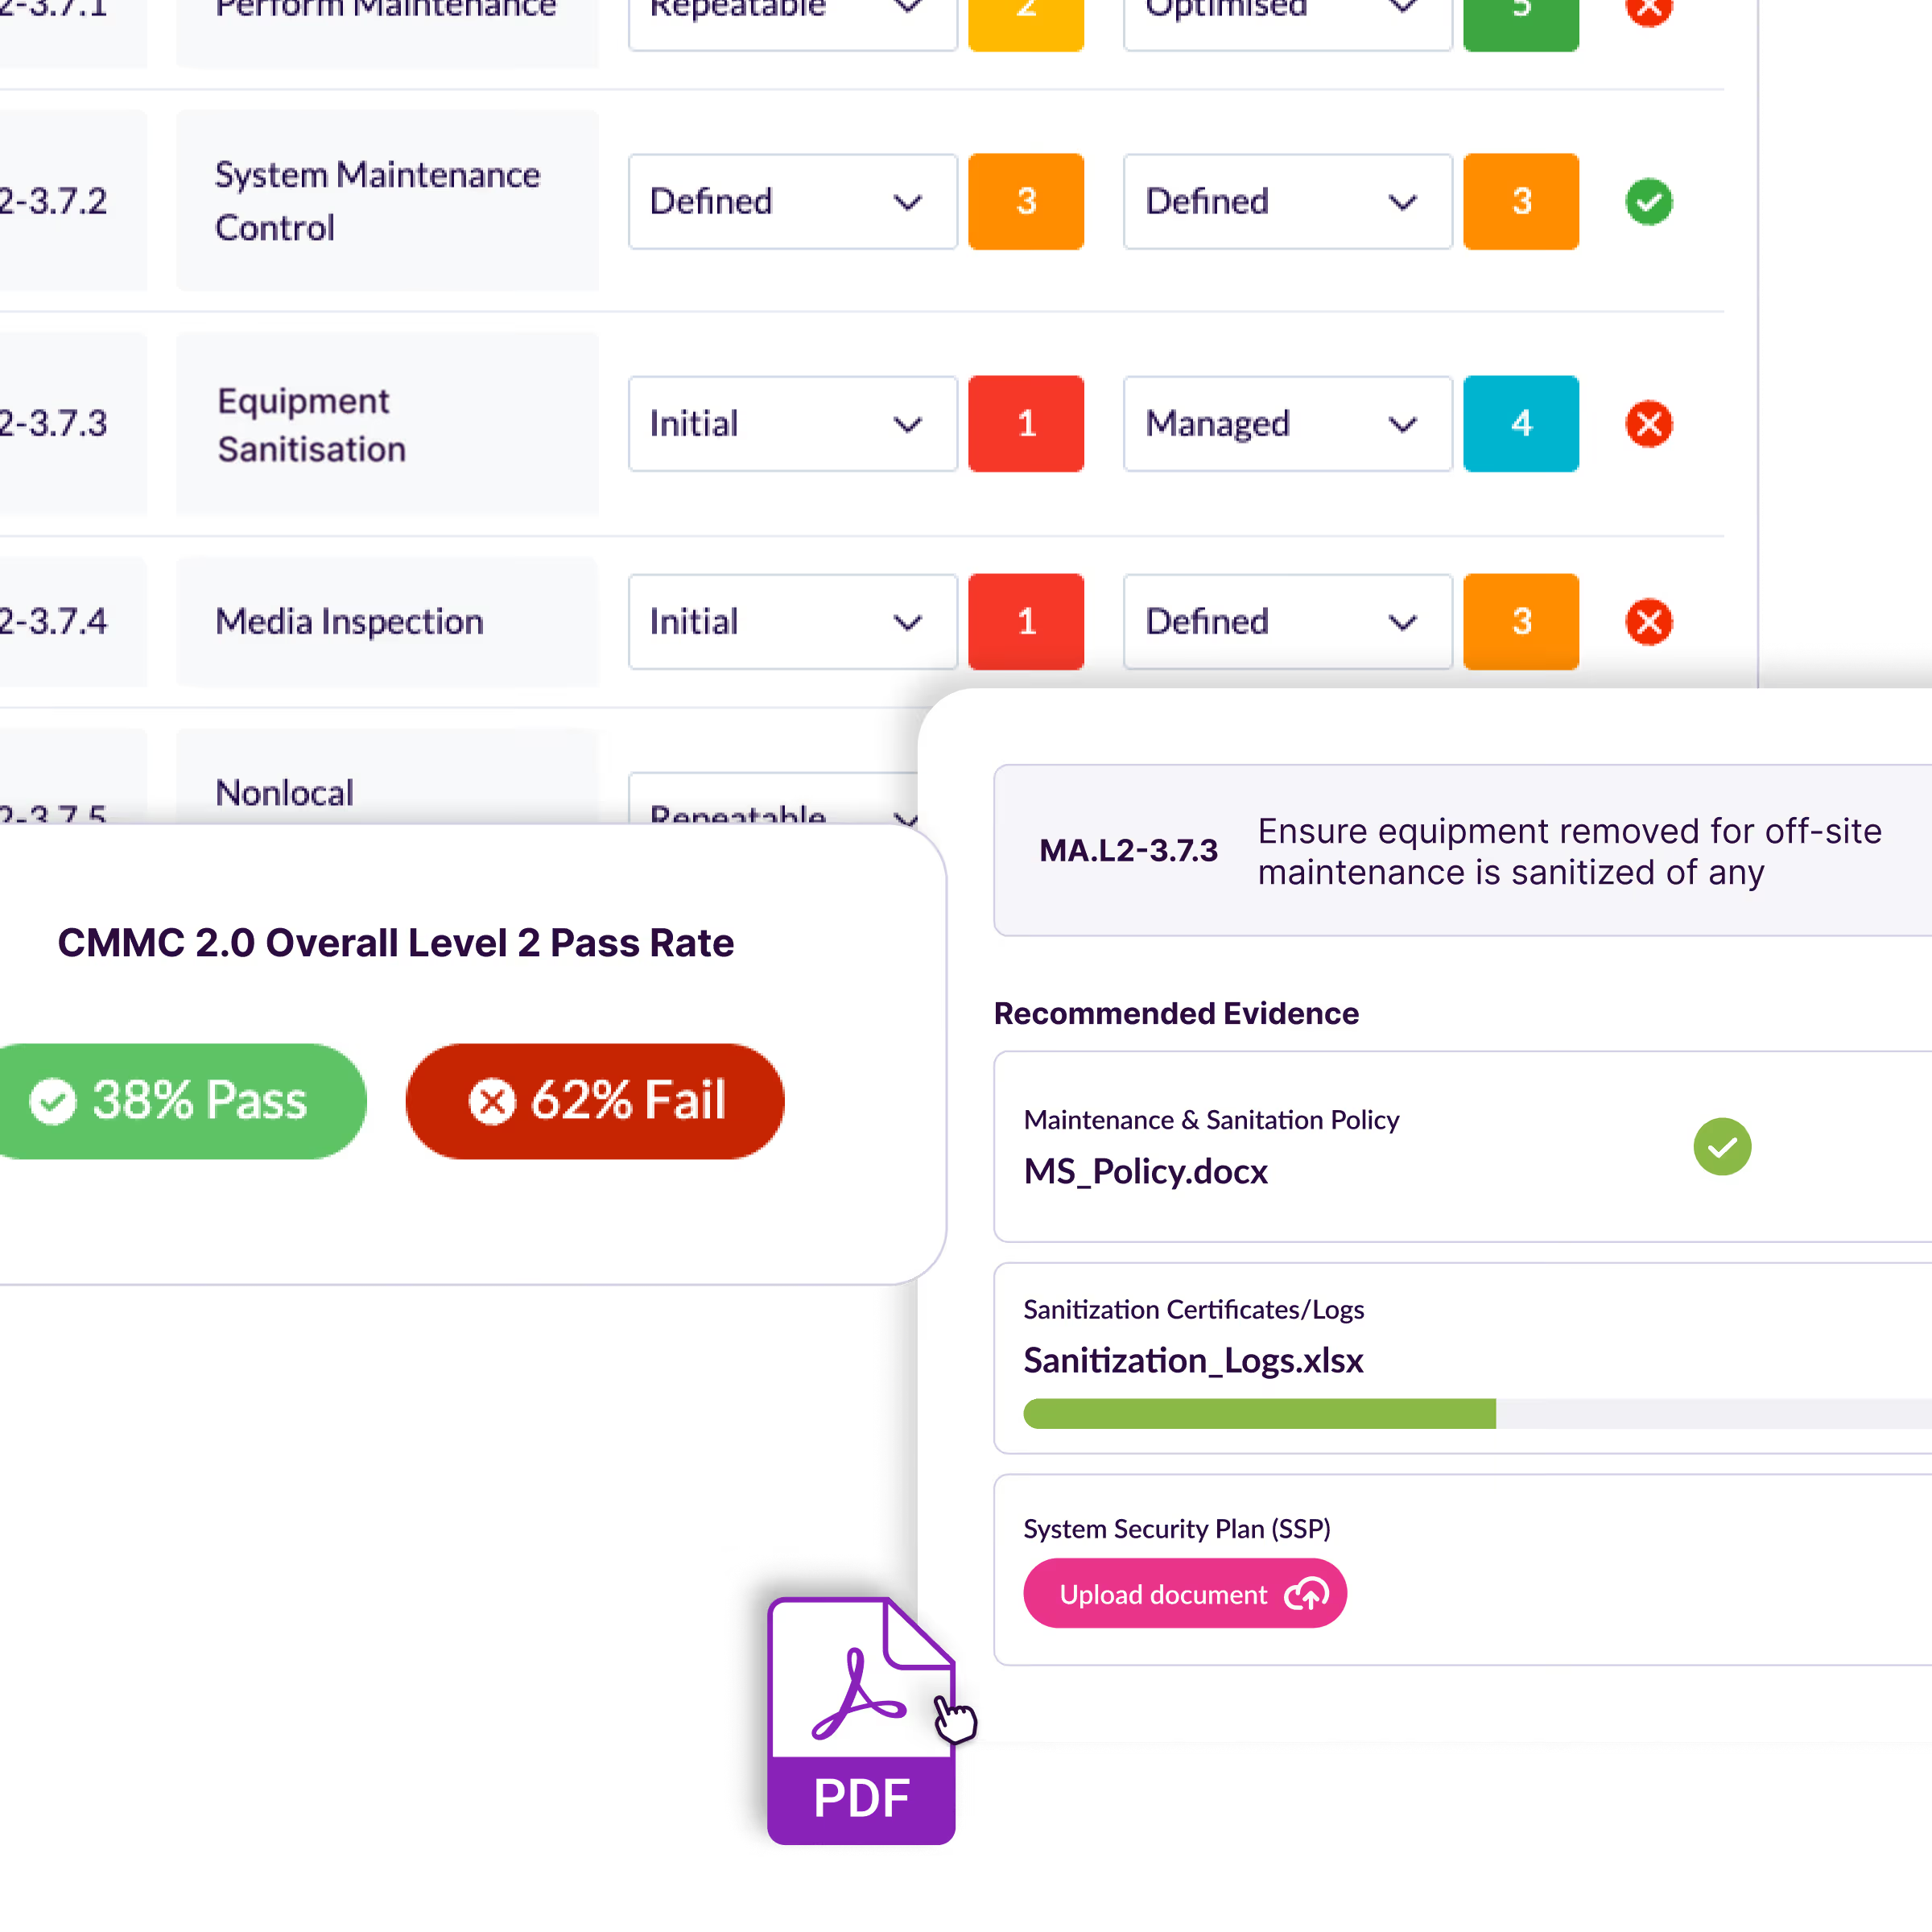
Evidence-Backed Confidence
CMMC 2.0 depends on more than declared practice. Confidence in readiness comes from being able to show how required practices are evidenced and how assessment judgements have been reached. In Spartacus Insights, evidence stays aligned to the relevant practice context, helping readiness remain clearer, more traceable, and easier to defend.
That improves review quality and reduces the ambiguity that often appears when evidence is handled separately from the assessment itself. Supporting material remains tied to the work it informs, making CMMC readiness easier to explain, review, and sustain over time.
This creates a more reliable basis for repeatable readiness across teams, cycles, and client engagements, while increasing confidence in both the process and the conclusions being reached.
Clearer Readiness Insight
CMMC 2.0 creates more value when organisations can clearly see where practices are strong, where weaknesses remain, and how readiness should be prioritised next. In Spartacus Insights, analysis, reporting, findings, recommendations, and improvement planning remain connected to the underlying assessment, helping turn CMMC activity into clearer readiness insight.
Approved outputs can be shared through controlled client access, while portfolio and trend views help show how results are changing across organisational scopes and repeat assessment cycles. This gives stakeholders a clearer view of priorities, progress, and where further readiness effort should be focused.


Built for Ongoing Confidence
CMMC 2.0 becomes more useful when it supports sustained preparation rather than a last-minute compliance scramble. Spartacus Insights helps preserve continuity across repeat assessment cycles, making the delivery model easier to sustain and results easier to interpret over time.
That continuity helps prevent loss of insight across delivery teams as programmes mature, while supporting a more repeatable and productised way to deliver CMMC. It also makes the process easier for clients to understand from the outset and easier to sustain over the longer term.
For consultancies, this supports stronger multi-year client relationships and a clearer route into follow-on improvement work. For internal teams, it provides a more durable model for managing CMMC readiness over time.
Where CMMC 2.0 Leads Next
CMMC 2.0 provides a strong reference point for understanding readiness, evidence confidence and priority areas for improvement. In Spartacus Insights, that insight extends into wider cybersecurity decisions, helping teams explore material risk exposure, strengthen supplier assurance, interpret protection against defined threat scenarios and shape more defensible control investment priorities.
More Than a Standalone CMMC Assessment
Spartacus Insights helps organisations use CMMC 2.0 as part of a broader and more connected cybersecurity readiness model. Assessment, evidence, analysis, reporting and improvement planning remain connected, making CMMC easier to deliver consistently and more useful as part of an ongoing readiness programme rather than a one-off review.
Where governed mappings and Capability Scores are available, CMMC evidence can also support Threats & Protection. This helps teams translate readiness evidence into threat-informed protection insight, recurring capability weaknesses and Evidence Completeness, while giving consultancies and internal teams a stronger basis for prioritised improvement conversations over time.
Explore More Frameworks
Different frameworks create different views of cybersecurity posture, readiness and assurance. Explore the Spartacus Insights framework set and find the right starting point for your programme.