NCSC Secure AI System Development
A Clearer View of Secure AI System Development
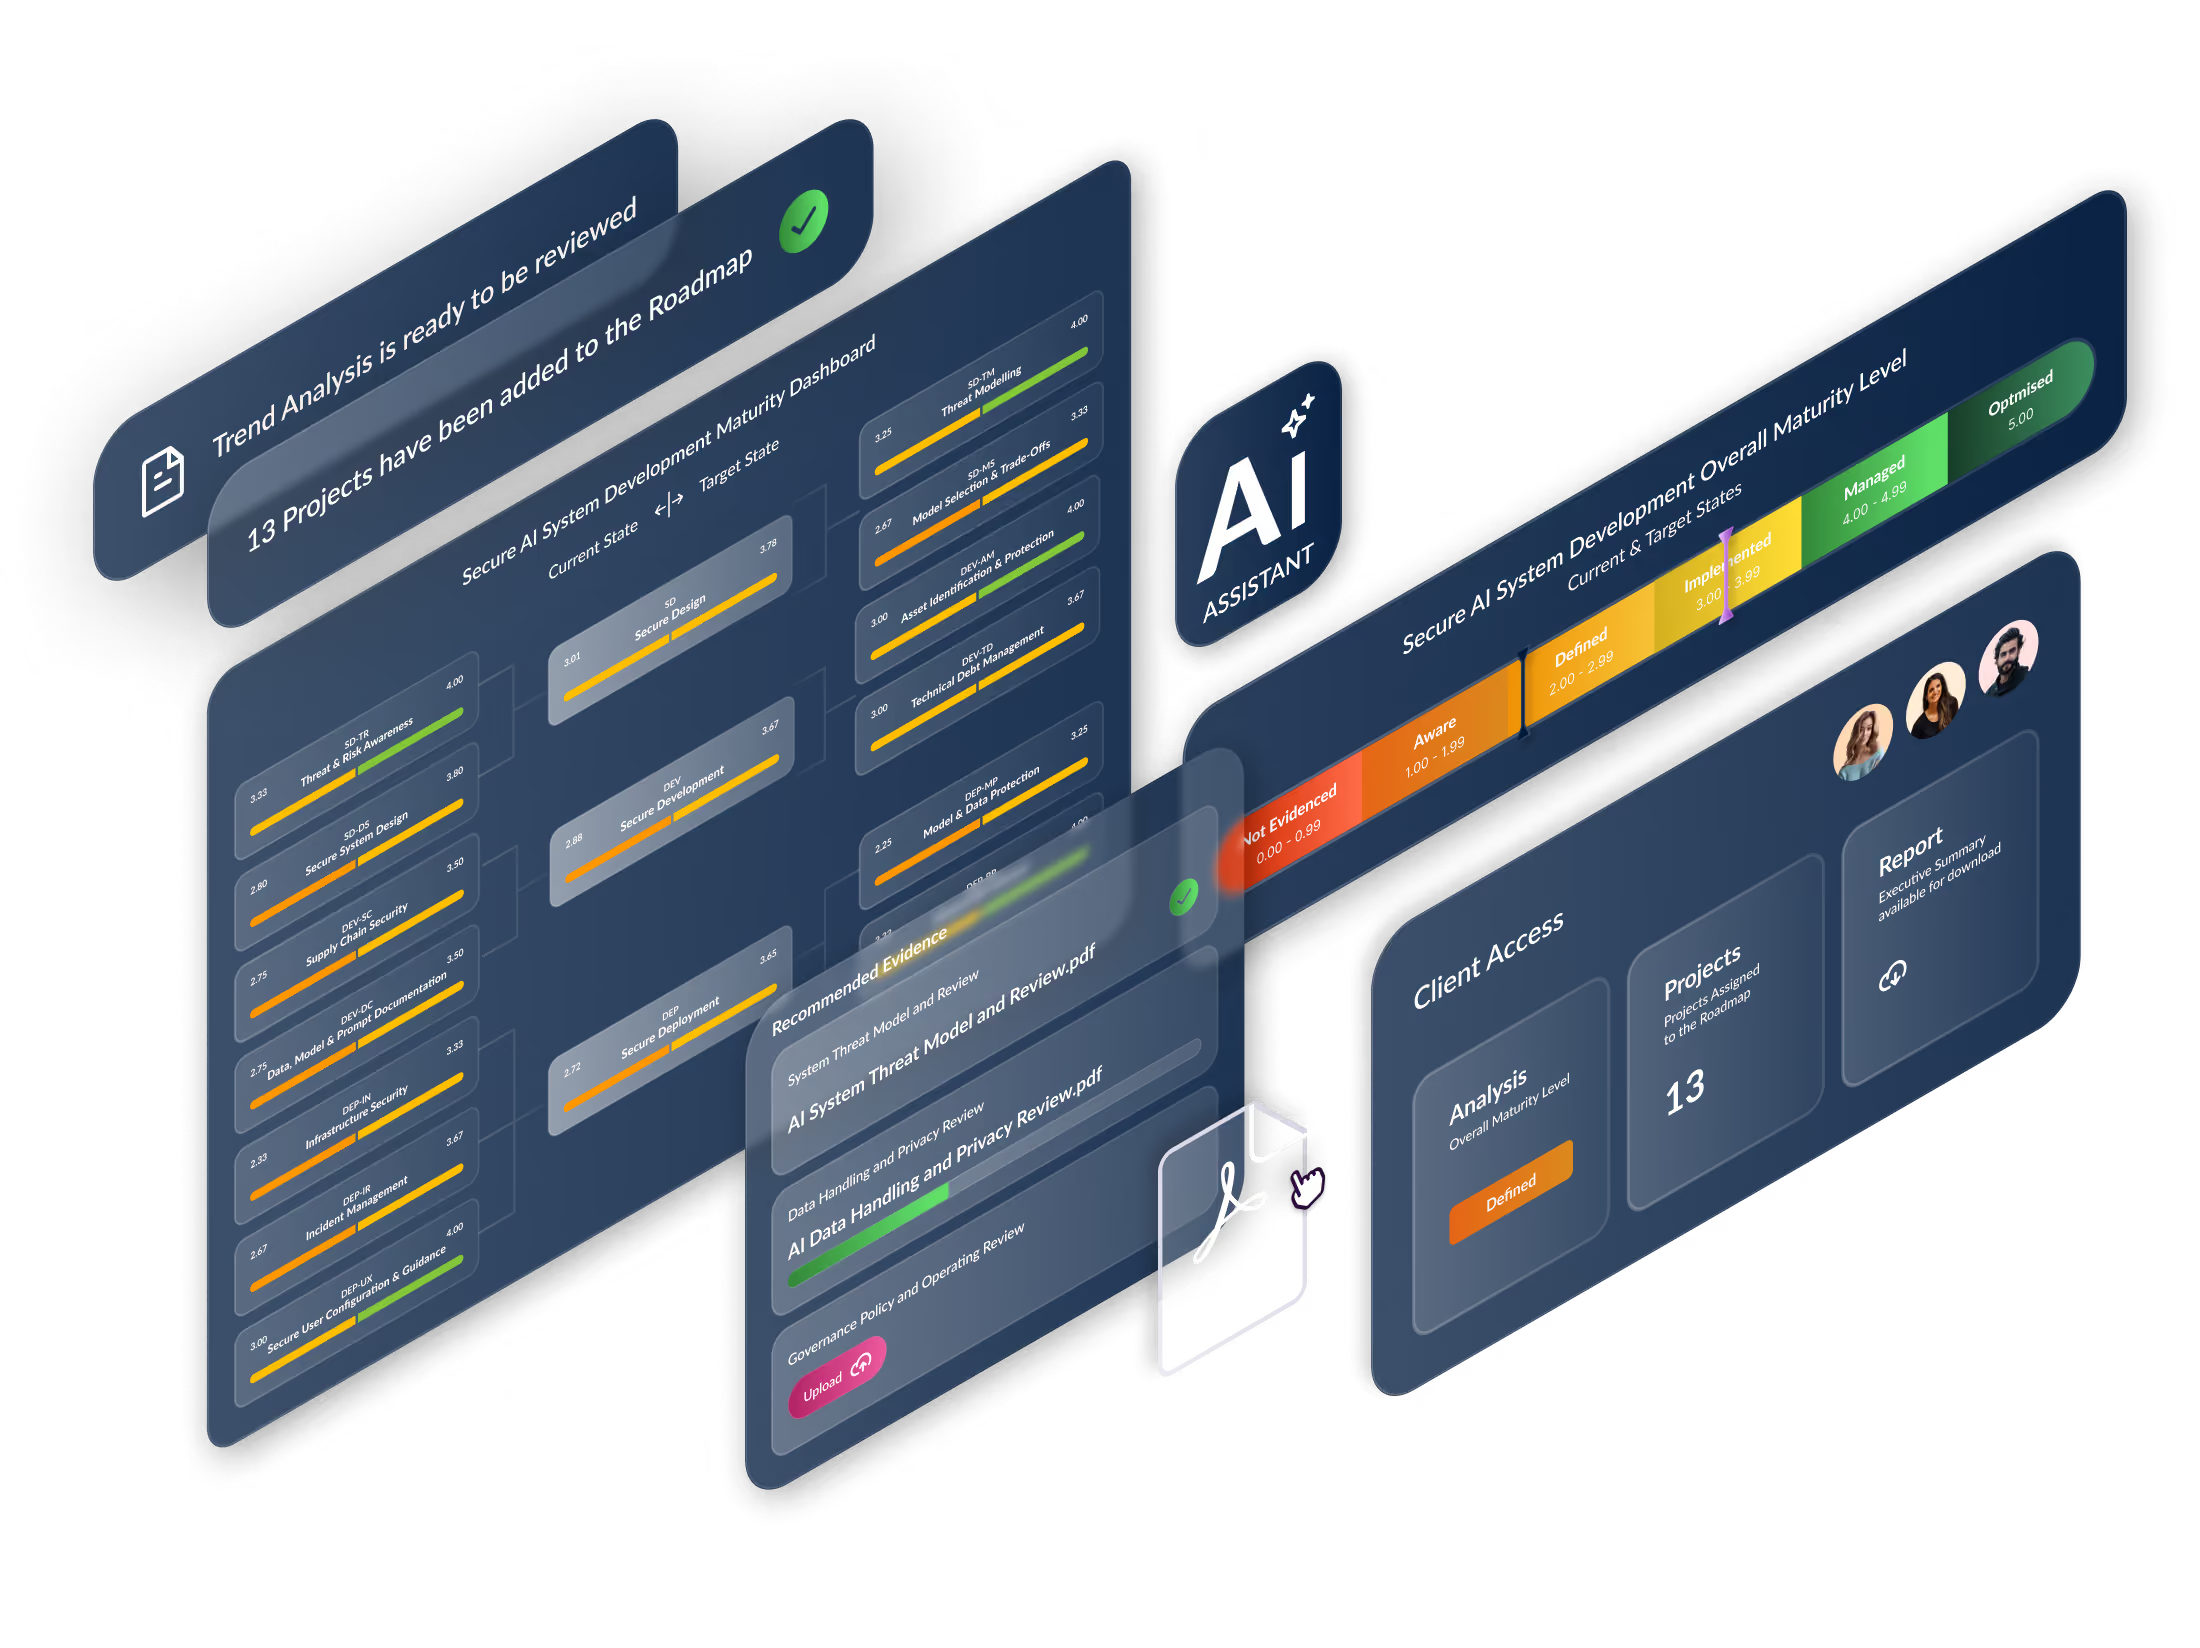
Understand how consistently security practices are applied across your AI system lifecycle. Spartacus Insights connects NCSC Secure AI assessments, evidence, analysis and reporting, helping teams explain strengths and weaknesses, agree priorities and justify improvements from design and development through deployment, operation and maintenance.
Why Organisations Use NCSC Secure AI
NCSC Secure AI helps organisations build security into AI systems and sustain it as those systems change. Aligned to NCSC’s Guidelines for secure AI system development, it brings together secure engineering practices, supplier dependencies and responsibilities across the lifecycle. This gives engineering, security and operations teams a shared basis for examining evidence, identifying weaknesses and agreeing improvements before deployment and throughout operation and maintenance.
Make Engineering Evidence Easier to Review
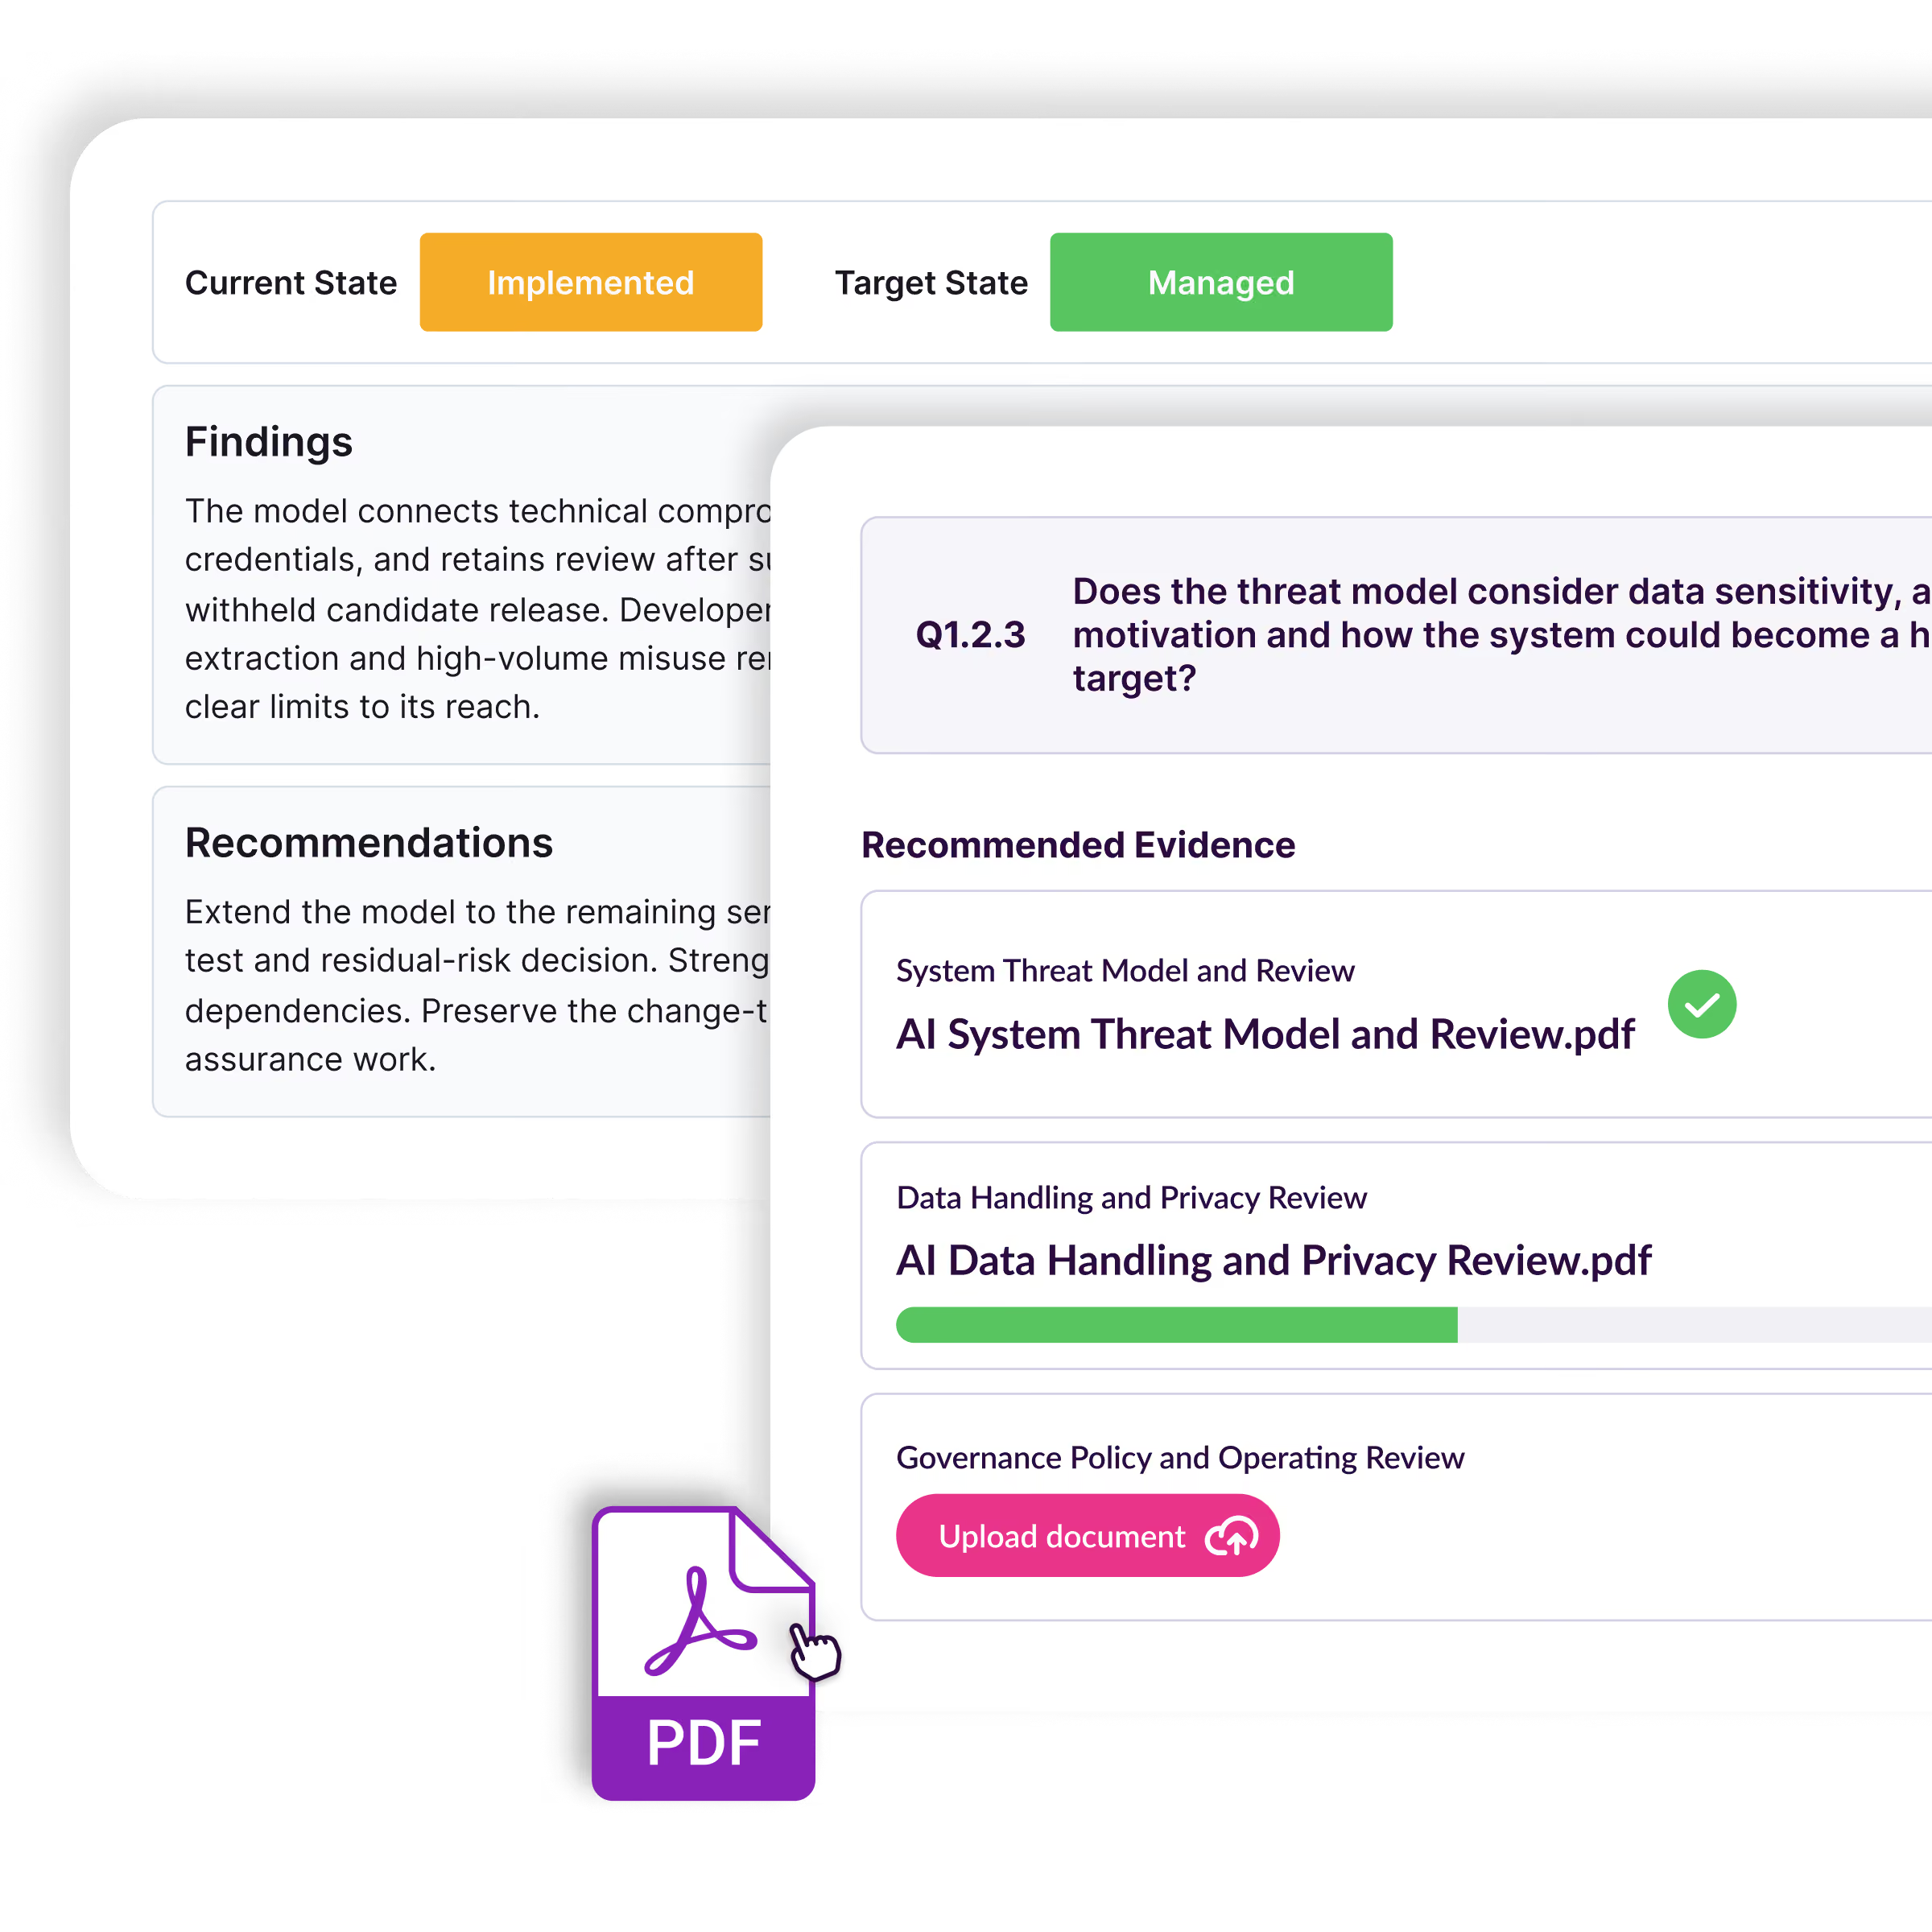
Architecture records, development decisions and operating evidence often sit across different teams and tools, making security judgements harder to explain. Spartacus Insights connects this evidence with assessment questions, findings and recommendations, helping teams substantiate conclusions, investigate gaps and preserve the reasoning behind decisions as AI systems change.
Build an Assessment You Can Explain
A credible secure AI assessment explains how security practices operate for the system and lifecycle stages in scope. Assessor guidance provides interview prompts, evidence suggestions, red flags and scoring guidance, helping teams challenge broad claims and examine actual engineering practice. Agreement on who provides and reviews evidence coordinates contributions across engineering, security and operations.
Linked documents retain findings and recommendations against each question. Notes capture design walkthroughs, demonstrations and discussions, preserving what was observed and any limitations. Assessors bring the evidence together into findings and recommendations for each assessment category, retaining responsibility for the conclusions and final scores.
Shared guidance supports consistent assessment under specialist oversight. Retained evidence and reasoning preserve system context through reviews and handovers, helping teams explain technical conclusions and identify where further investigation or specialist testing is needed.
Choose the Right Assessment Scope
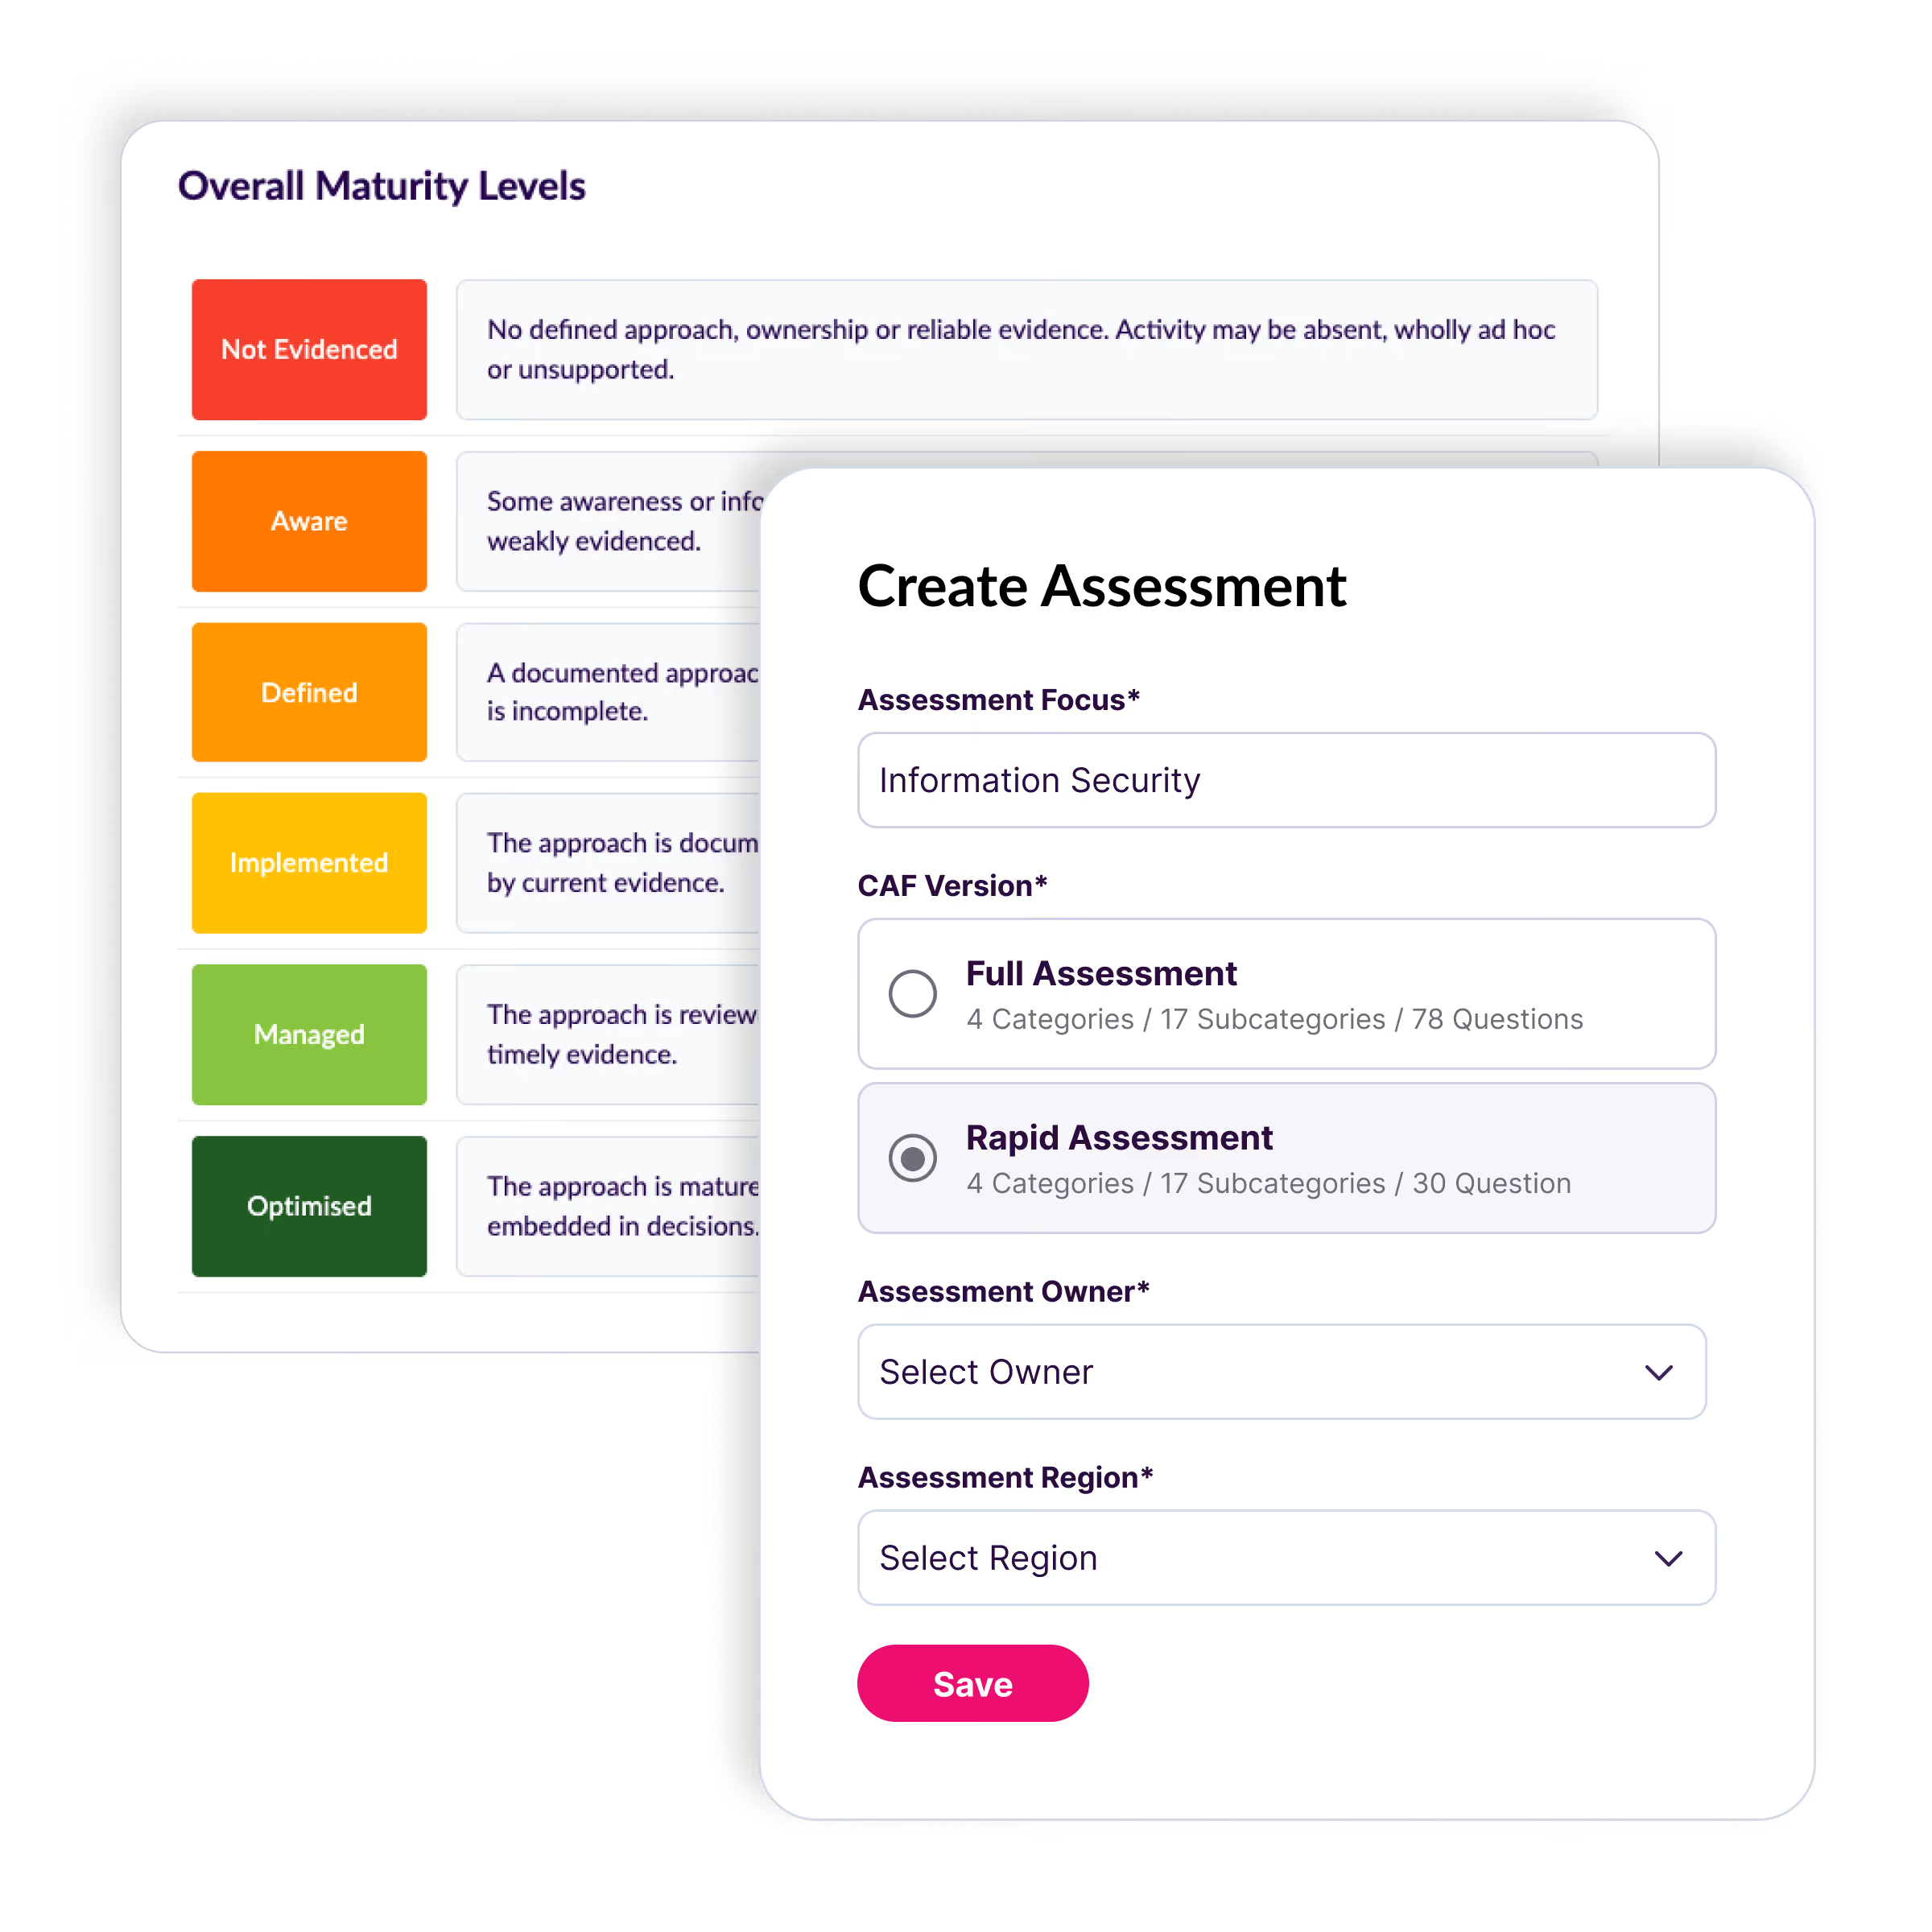
Choose a Full assessment for the complete question set or a Rapid assessment for a focused initial review. Agree the system and lifecycle stages in scope, whether reviewing a planned deployment, an operating system or material change. Rapid conclusions remain limited to the areas assessed.
Both use Spartacus Insights’ 0–5 maturity scale, from Not Evidenced to Optimised, to compare current secure development practice with agreed targets and identify where improvement is needed.
Turn Lifecycle Weaknesses into Engineering Priorities
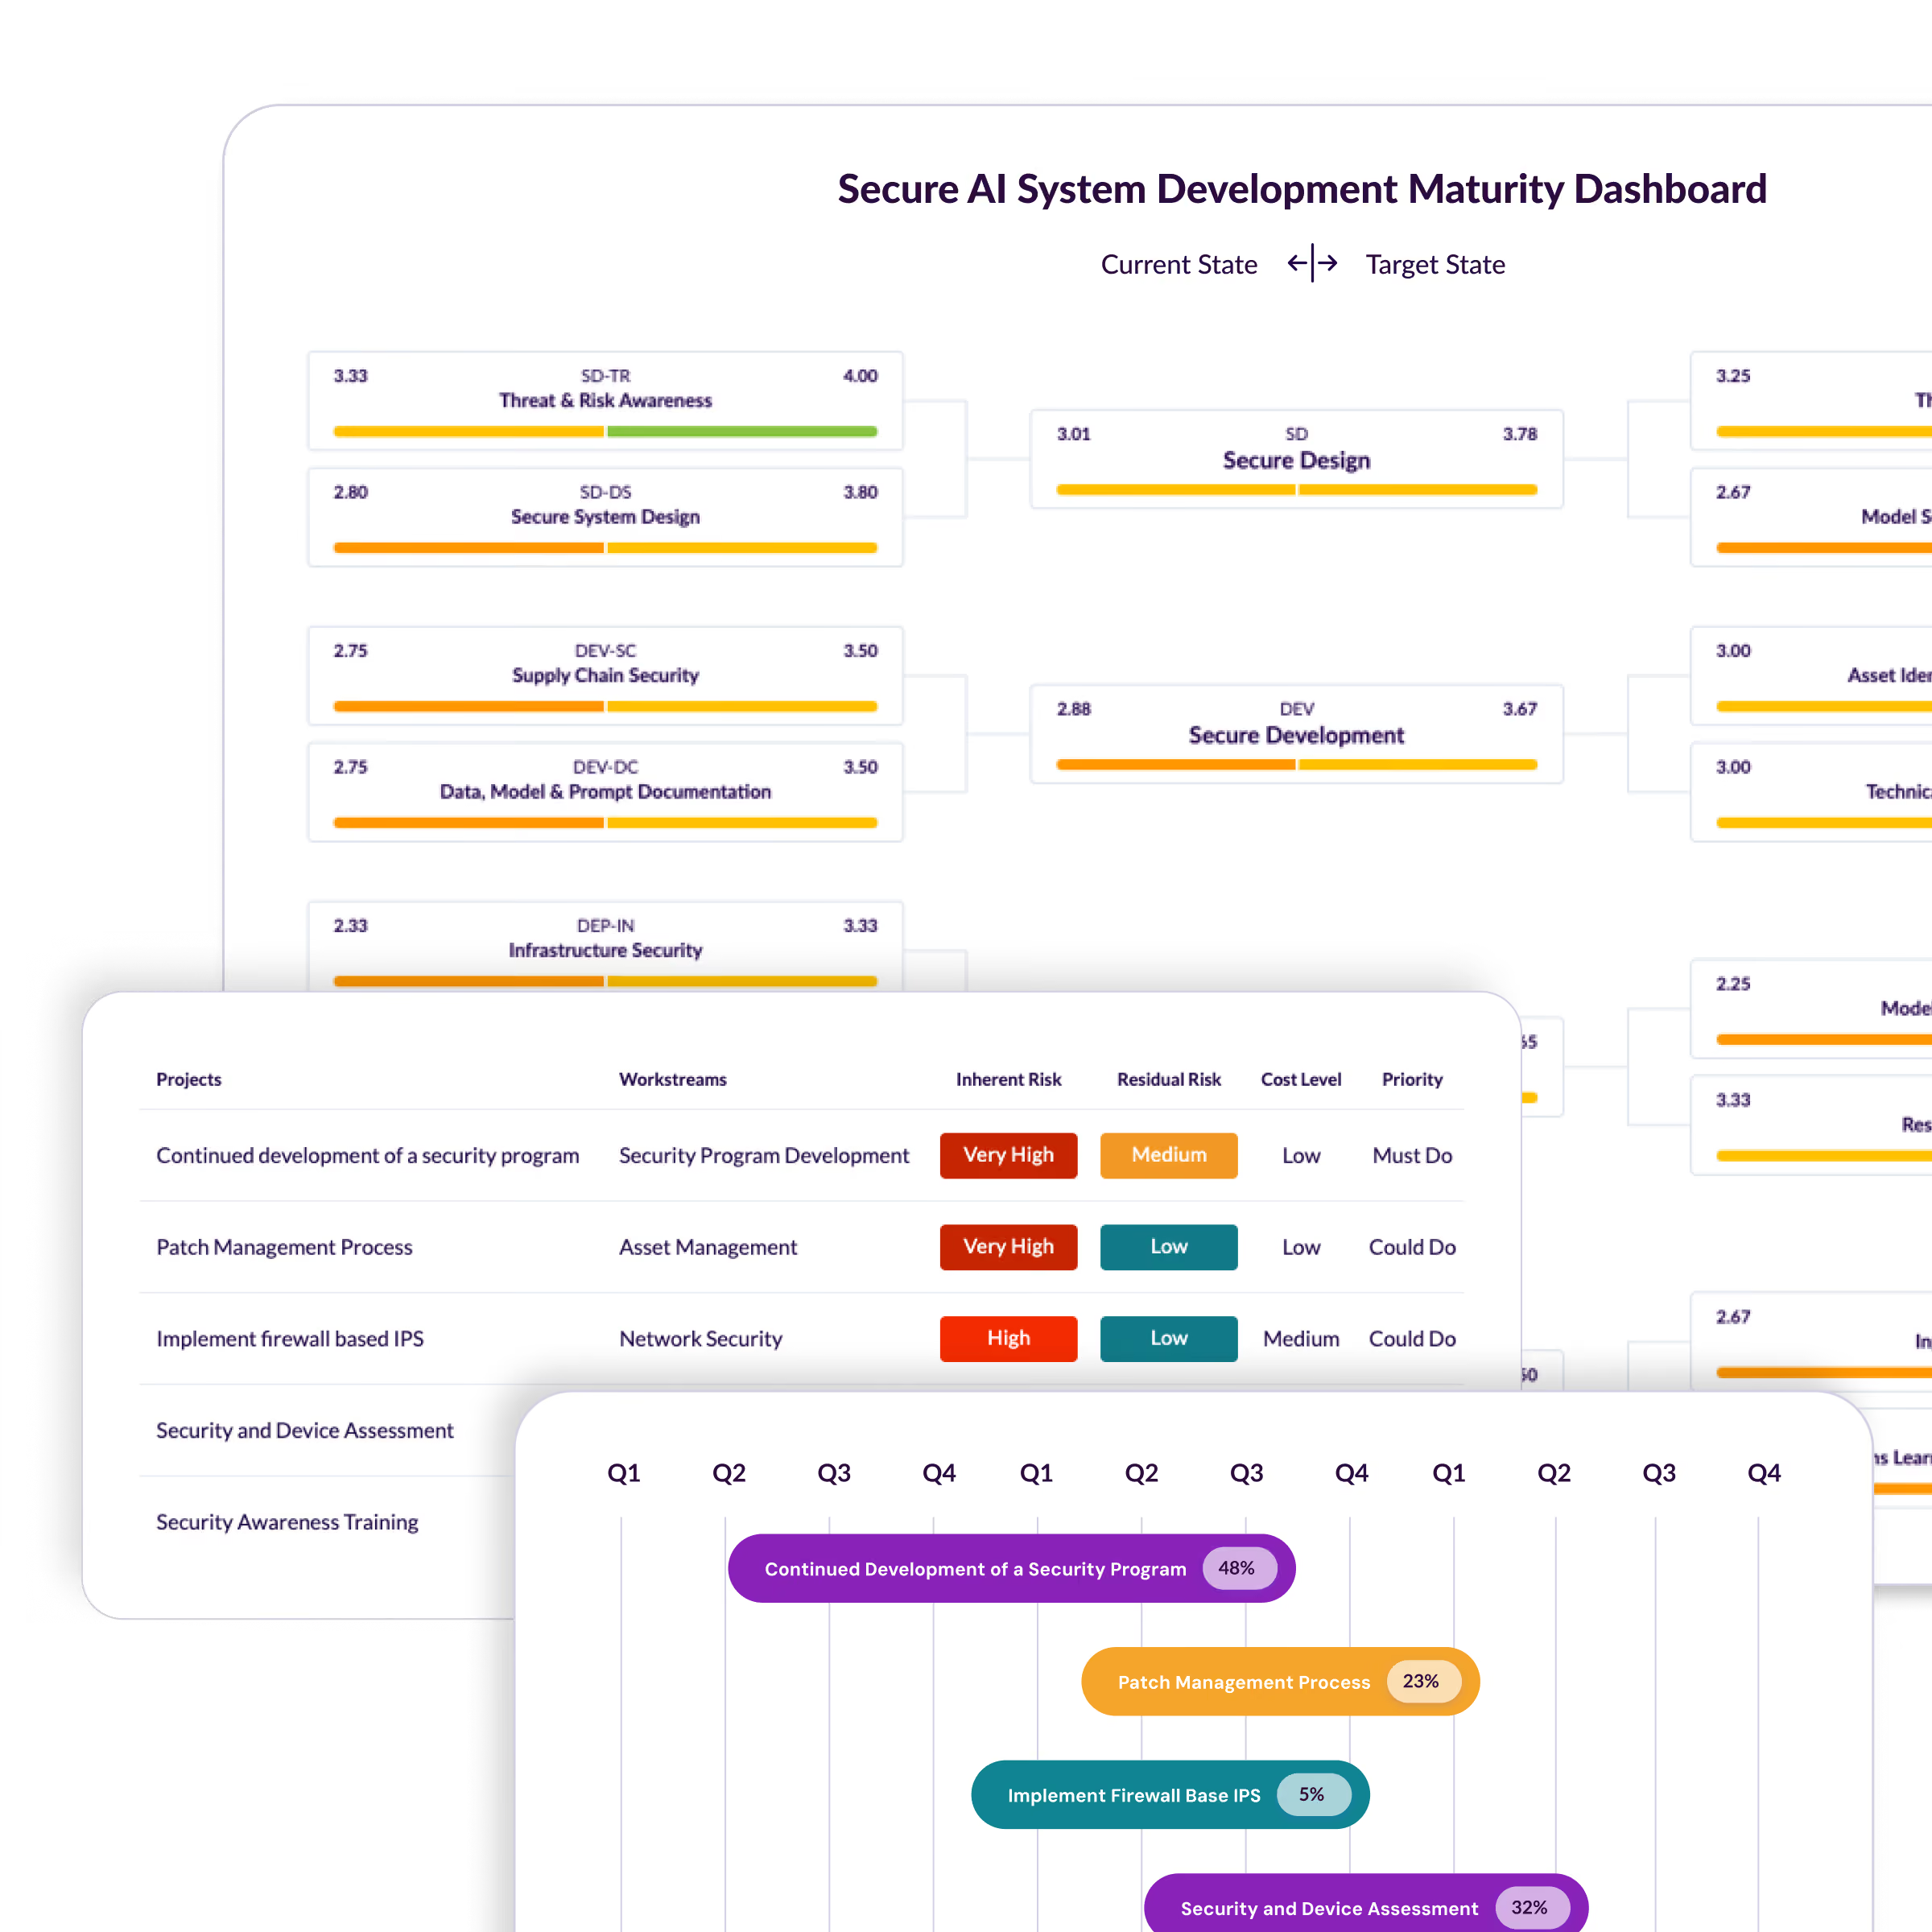
Heatmaps and charts reveal gaps between current and target maturity across the AI system lifecycle. Teams can examine the underlying questions, scores and evidence to identify weak security practices or unclear responsibilities between teams and suppliers. This helps distinguish assessed weaknesses from gaps in supporting evidence and target further investigation.
Improvement proposals connect those findings with expected benefits, deliverables, resources and estimated costs. Workstreams and timelines organise the proposed programme across engineering, security and operations, giving sponsors a clearer basis for coordinating work, comparing priorities and deciding which improvements to fund.
Reports explain technical findings and their implications for management. Analysis graphics populate relevant sections automatically, while seeded report content and consultant instructions reduce preparation effort. After review, teams can share interactive reports or branded PDFs. Controlled Client Access lets stakeholders revisit selected read‑only outputs and discuss the proposed work, while internal evidence, notes and drafts remain private.
Reassess as AI Systems and Dependencies Change
Changes to models, data, suppliers, deployment or operating arrangements can alter the basis of an earlier assessment. Reassessment helps teams establish whether security practices remain appropriate, how close they are to agreed targets and which weaknesses still need attention.
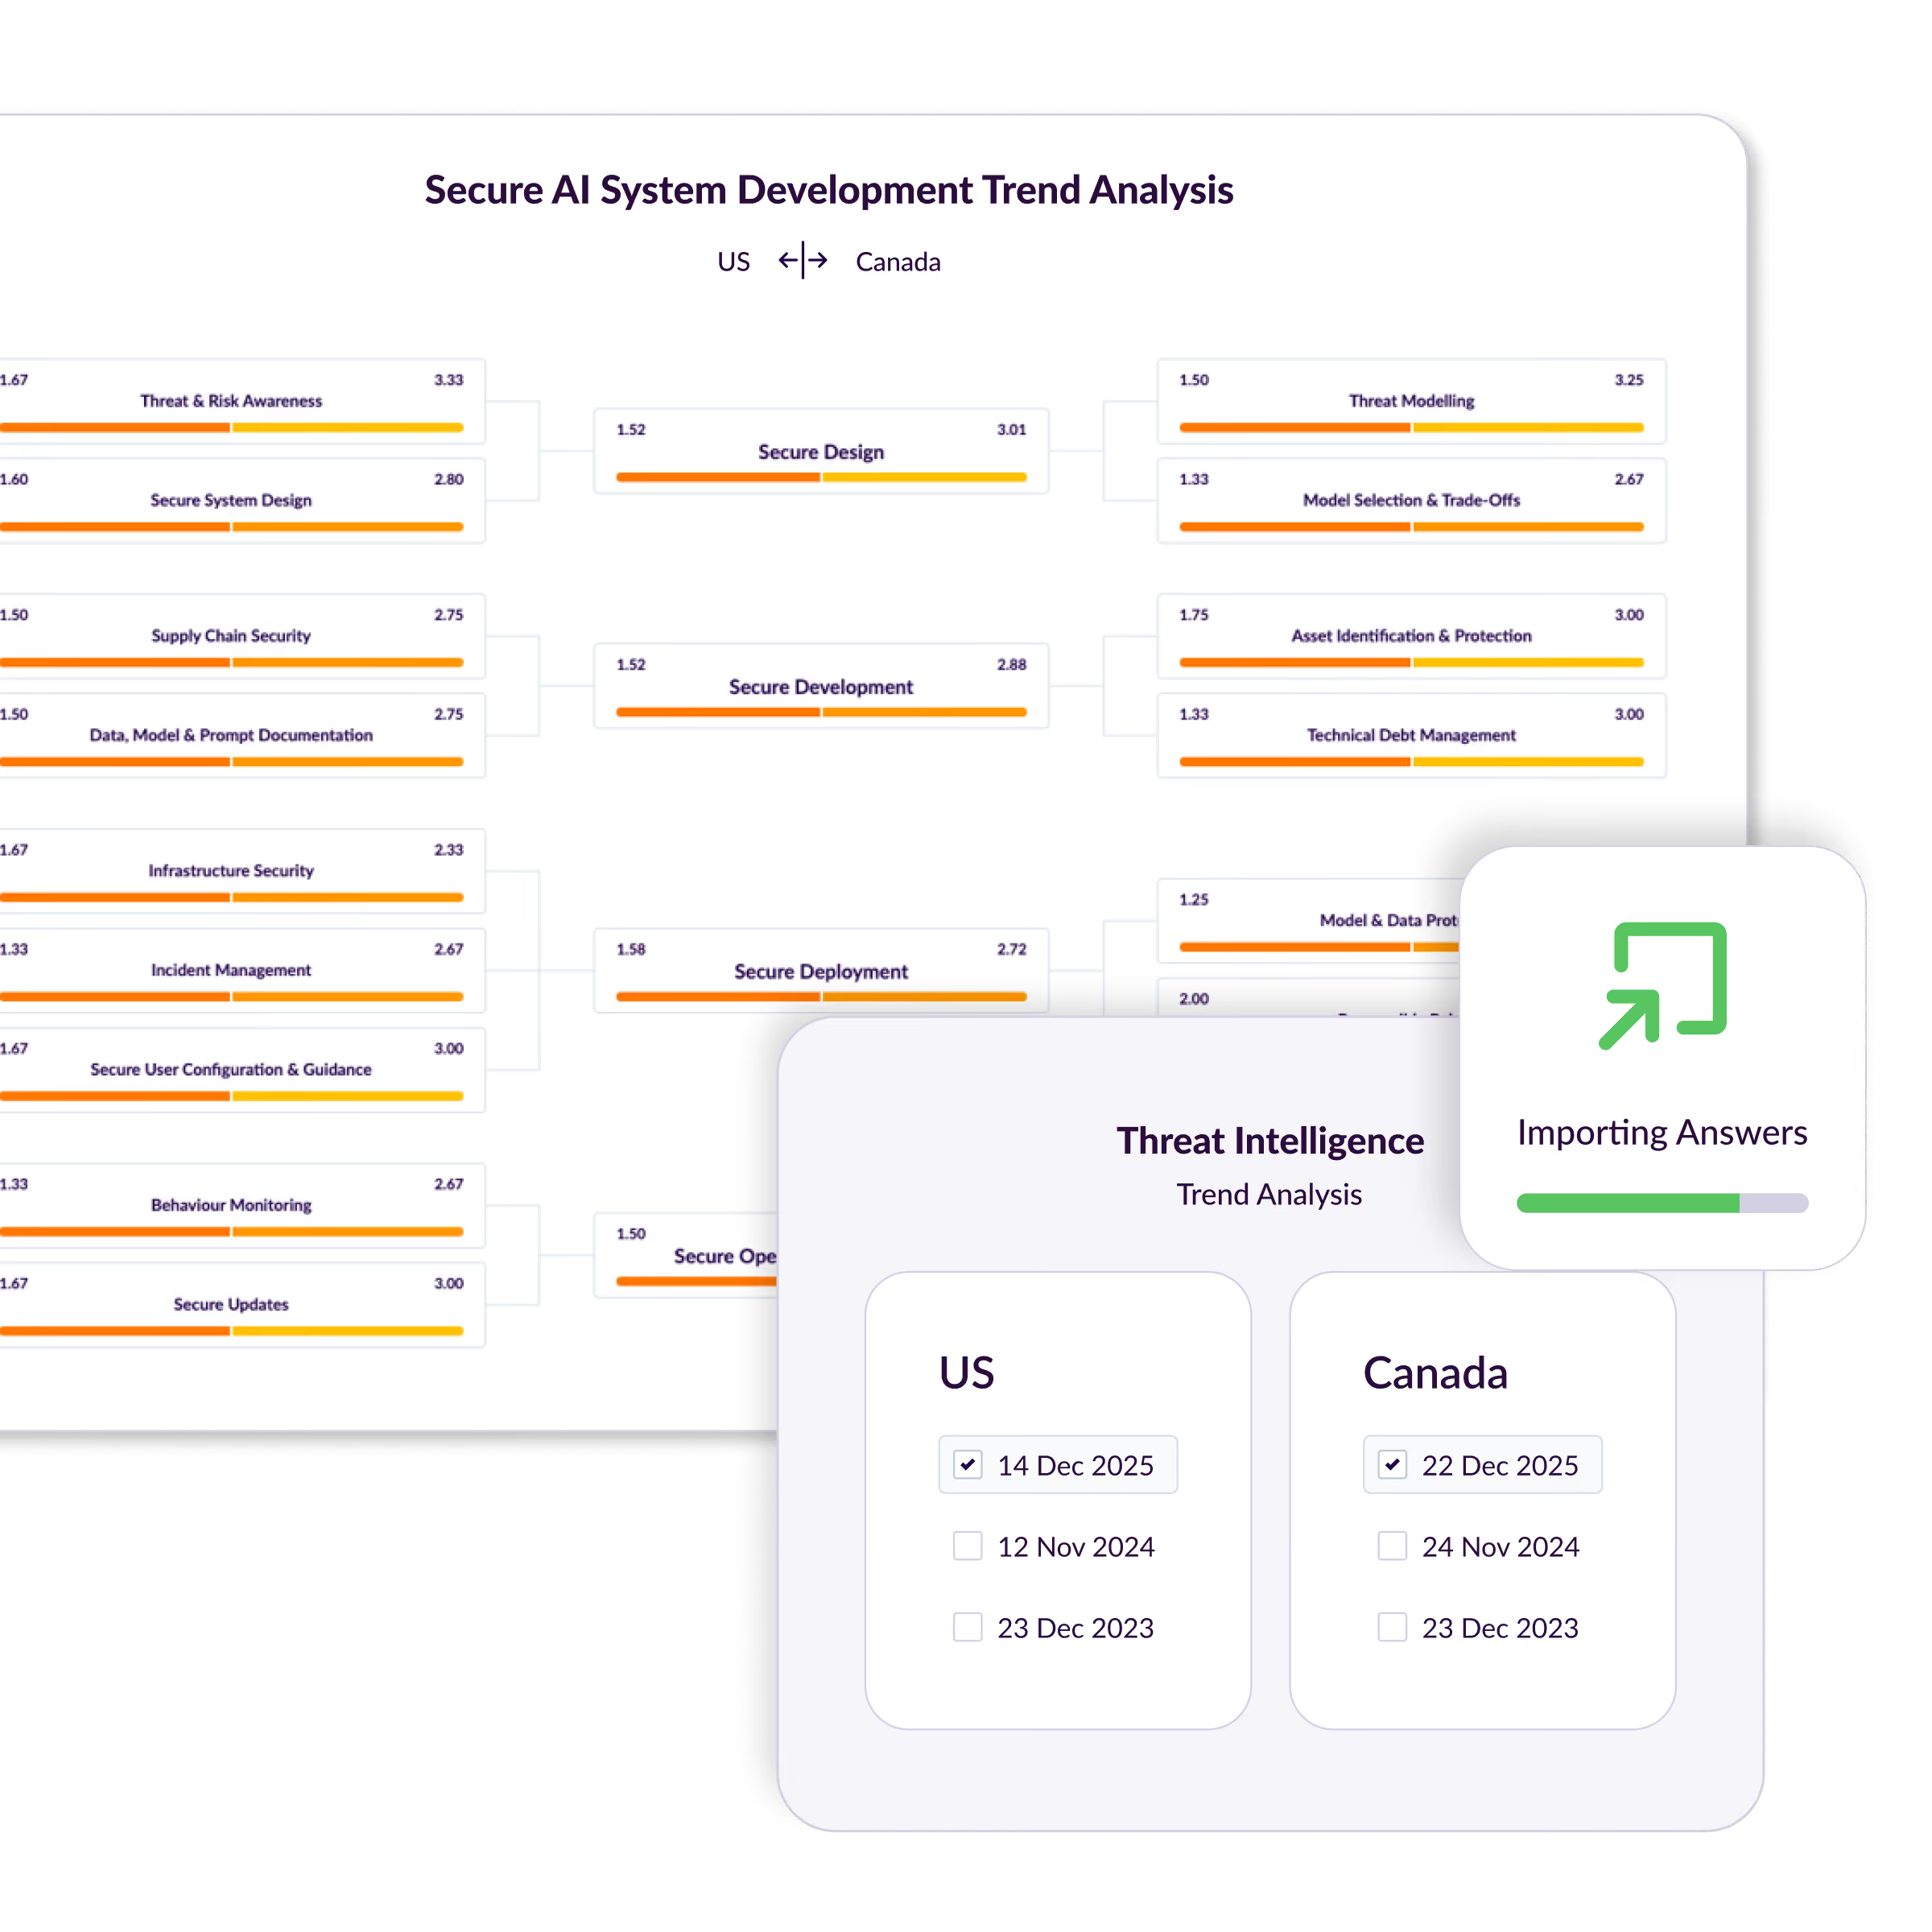
Trends brings selected NCSC Secure AI assessments together to compare results over time or across business areas and regions. Meaningful comparisons account for framework versions, question sets, scoring definitions, system scope and evidence periods. This helps leaders identify recurring engineering weaknesses, distinguish them from system‑specific issues and prioritise improvements across teams.
Connect Secure Development with AI Risk Oversight
NCSC Secure AI findings may raise questions about who owns AI risks and how decisions are reviewed. A complementary NIST AI RMF assessment examines accountability, system context, risk evaluation and oversight. Each retains its own scope, evidence, scores and report, while related findings help teams connect engineering improvements with governance priorities.
Build Repeatable Secure AI Assurance
Spartacus Insights helps consultancies deliver repeatable secure AI assessments and translate technical findings into clear advice for stakeholders. Shared guidance and structured reporting reduce repeated preparation while preserving the context of each system. Findings provide a basis for secure development advice, supplier assurance and continuing reassessment.
Internal teams gain a shared basis for examining security practices and explaining improvement needs across engineering, security and operations. Retained evidence and assessment reasoning preserve knowledge through handovers, helping teams answer assurance queries and maintain oversight as systems, suppliers and delivery responsibilities change.
Explore More Frameworks
Different frameworks create different views of cybersecurity posture, readiness and assurance. Explore the Spartacus Insights framework set and find the right starting point for your programme.